Red Team
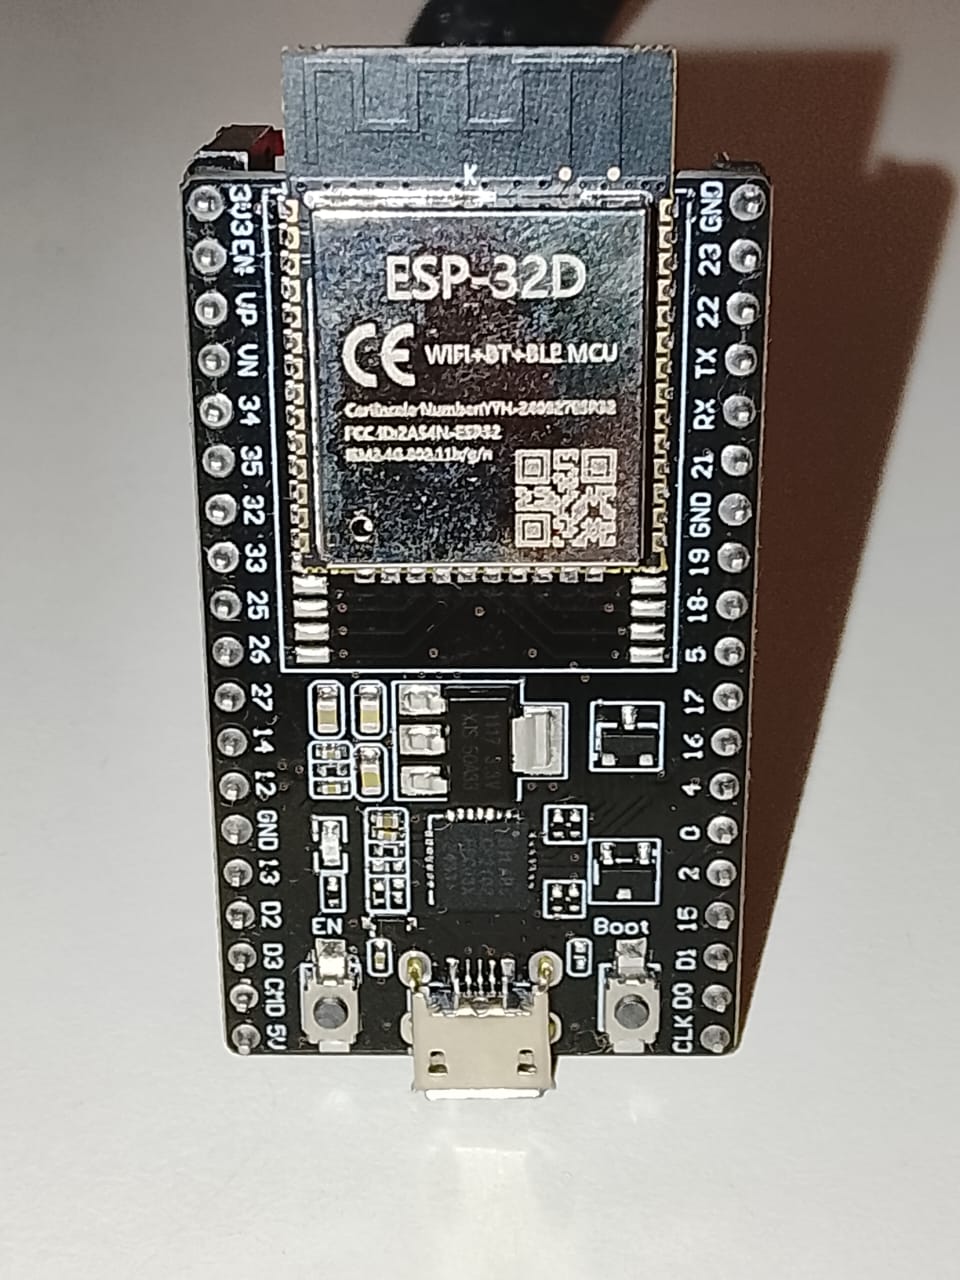
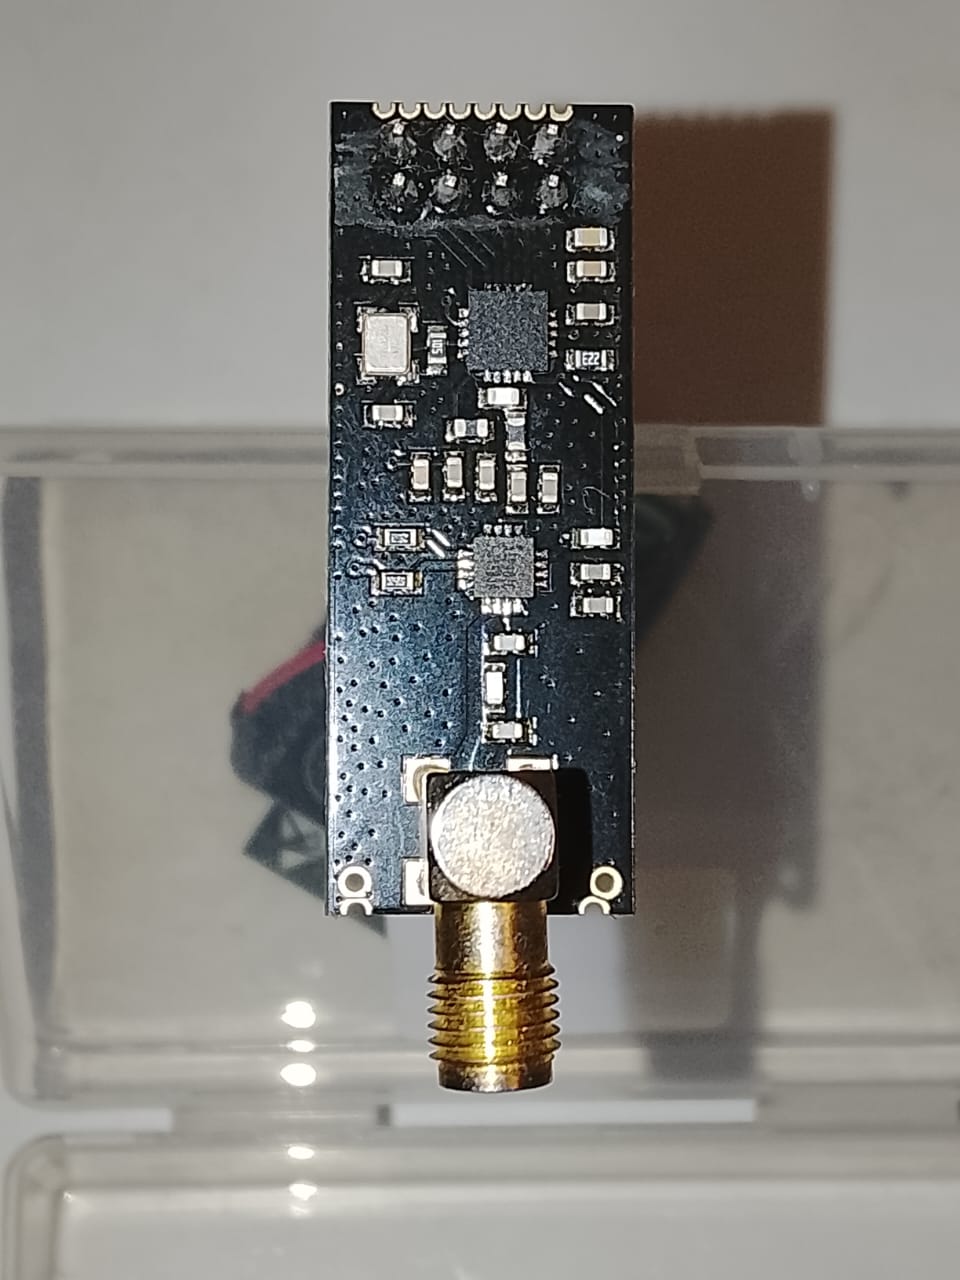
Simulates authorized attacks within a defined scope to test an organization's defenses.
Red teamers think like attackers: they probe networks, applications and people — through phishing and social engineering — for real weaknesses, always inside a legal, pre-agreed scope, then report what they found so it can be fixed before a real adversary finds it first.